Kai Castledine KSEC Group
Get in touch

Offensive security and founder

Hi, I'm Kai Castledine.

Offensive security practitioner, from pentesting to red teams, now building the tools and training the industry uses.
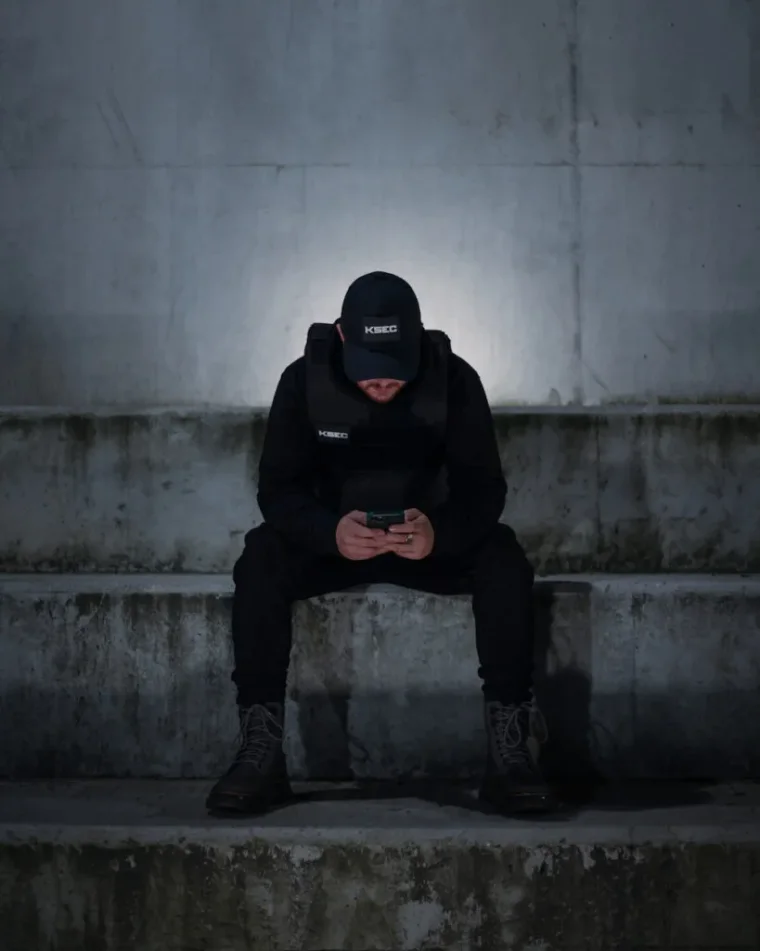
Kai Castledine

About

Security is a human problem

I work at the intersection of security, entrepreneurship and hands-on advisory. KSEC was founded on a simple idea: real security starts with understanding, not just of systems, but of the people who use them. That philosophy has shaped everything I have done since, from building businesses and security service platforms to developing tools that empower individuals and organisations alike. I believe security is more than a technical challenge, it is a human one, and often the biggest breakthroughs come from the spaces between disciplines.

Offensive security

Nine years breaking things so other people don't have to

I spent nearly a decade on the offensive side, first as a consultant at Context Information Security (now Accenture Security) and then as Head of Offensive Security at Informer, where I led the pentest team. Over that time I have found and reported tens of thousands of vulnerabilities, and the work has not stopped. These days hacking is how I wind down: independent research and vulnerability disclosure, alongside running the group.

Web applications and infrastructure are often where it starts, not where it ends. Chaining findings from external testing is how an engagement turns into internal compromise.

Full-cycle compromise

Engagements run end to end and mapped to MITRE ATT&CK: reconnaissance, initial access, lateral movement and privilege escalation through to the objective.

Bespoke RFID cloning

Reading, cloning and emulating access credentials, including proprietary and custom systems that off-the-shelf tools do not cover.

Covert physical jobs

Surveillance, pretext and entry, placing implants and getting out unseen, to show what a determined intruder could actually reach.

Anatomy of a compromise

  1. ReconnaissanceForgotten staging site found in certificate logsInfo
  2. ReconnaissanceStaging API leaks the staff directoryLow
  3. Initial accessPassword spray finds a seasonal password on the VPNMedium
  4. Credential accessService account ticket cracked offlineMedium
  5. Privilege escalationDelegation misconfig to domain adminCritical
  6. PhysicalBadge cloned in the car park opens the comms roomMedium
  7. ExfiltrationCrown-jewel data taken outCritical

Illustrative, built from patterns seen across engagements. No single client. Labels are MITRE ATT&CK tactics, apart from the physical step, which ATT&CK does not cover.

Selected engagements

  1. Healthcare, multinationalFrom a compromised Remote Desktop terminal server to domain admin across a multinational healthcare provider. The same route has worked at other organisations since.
  2. Medical devicesA connected medical device led into its cloud health-data integration, and a local privilege escalation plus credential reuse opened a route across the network before testing was paused to remediate.
  3. MaritimeA shipping-sector platform taken from low-privilege user to administrator, with widespread account compromise. Evidence of wider threat activity was found and reported.
  4. Critical infrastructureA physical assessment at a regulated critical infrastructure site, from outside the perimeter to the upper floors, then on to undocumented weaknesses in internal network devices.
  5. TransportA large transport organisation worried about social engineering. Several routes around the web application's restrictions came from a mobile API backend that did not enforce the same rules.

What I test

  • Web applications and APIs, including business logic
  • Mobile applications, iOS and Android
  • External and internal infrastructure
  • Active Directory, domain trusts and estate configuration
  • Cloud platforms: AWS, Azure and GCP, and hybrid estates
  • Wireless and RFID, access control and embedded hardware
  • Red team and attack simulation, from rogue insider to physical entry scenarios
  • Bespoke and complex architecture that does not fit a standard methodology

Some of where I have worked

Aviation, banking, insurance, defence, government, nuclear, maritime, critical national infrastructure and FTSE 100 companies.

Research and community

  • Wrote internal testing methodologies for RFID, physical red teaming and cloud (AWS and Azure)
  • Biohacking workshop at DEF CON 2019
  • Maintain TagBase and a set of online pentesting resources

Where I started: Advanced Infrastructure Hacking, hands-on lab certifications, Physical Red Team Operations and Social Engineering Expert, AWS and Azure certifications, and Microsoft networking and server accreditations from my IT support years.

How I approach it

  1. Think like the attacker, report like the defender. Findings only matter if the people fixing them understand the risk and the fix.
  2. Chain the small things. Most real compromises come from three low-severity issues lined up in the right order, not one critical.
  3. Scope to the real threat model. A nuclear site and a fintech startup should never get the same test.
  4. Physical and digital are one attack surface. A cloned badge or an unlocked comms room can bypass overlooked lines of defence.
  5. Explain it to the board. Translating technical risk into business decisions is a skill in its own right, and the one most often missing.
Scope an engagement with KSEC Advisory →

Today

Running the group, seven days a week

These days the attacker's mindset goes into building and running the businesses. I lead the teams and own the operations across the KSEC group: the UK and European stores, trade and government accounts, the OnlySecurity training platform and the BSides Brighton community. Customers worldwide means the work does not keep office hours, so neither do I.

Lead

Setting direction across the group and leading teams from legal and finance to operations and the warehouse, in the UK and Belgium, while staying close to customers, suppliers and brand partners.

Build

Hands-on engineering across the stack: shared infrastructure and hosting, DevOps, custom platform code, and the integrations that tie stores, logistics, finance and support together.

Operate

Day to day ownership of a global operation, from stock, shipping and customs across borders to compliance, finance and keeping every site up.
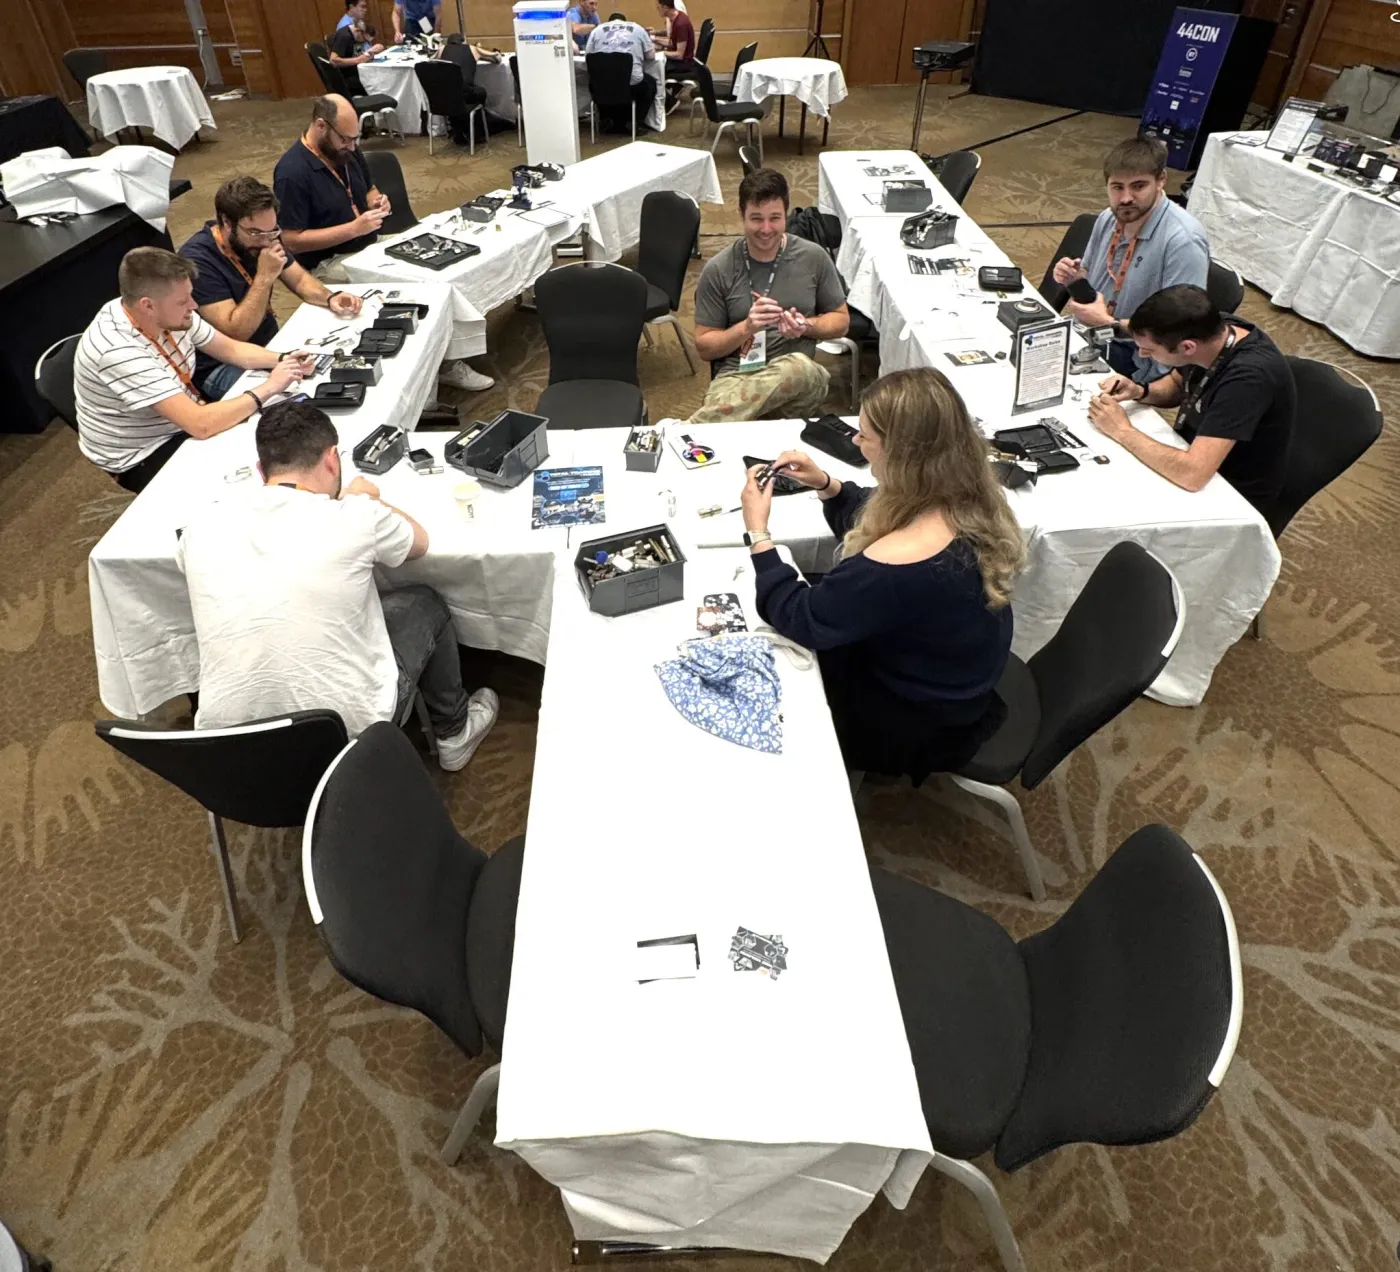
Lockpicking workshop tables at 44CON, attendees working on locks
Lockpicking workshop, 44CON
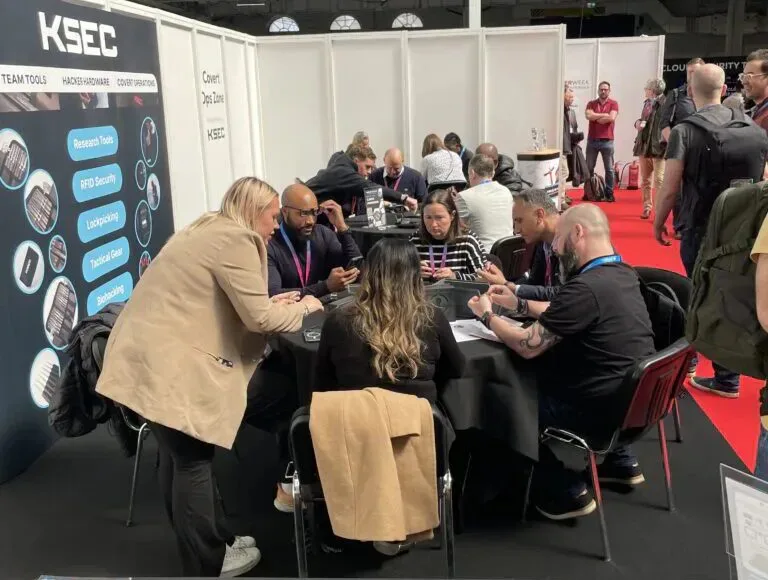
Hands-on workshop at the KSEC stand, UK Cyber Week
Hands-on workshop, UK Cyber Week

Trusted in the field

KSEC equipment is supplied to teams at FTSE 100 defence primes, S&P 500 aerospace and technology firms, UK and US Government, police and emergency services, the NHS and the Big 4 consultancies.

Customer names are withheld out of respect for their procurement and disclosure policies.

Engineering

  • Infrastructure and DevOps for every site in the group, run in-house on our own servers
  • Custom code: platform features, checkout and delivery logic, internal tools and admin systems
  • Data and reporting: one pipeline from the stores, finance and logistics into live dashboards
  • AI-led engineering: multi-agent development with security, correctness and performance review gates before anything ships
  • Integrations across ecommerce, accounting, shipping, email and support platforms
  • Security on our own estate: the same offensive thinking applied to everything we build, and shared with the wider team

Business

  • European expansion: KSEC EU, run from Belgium, with multi-language and multi-currency stores
  • Wholesale, trade and government accounts
  • Brand and supplier partnerships
  • Training and events, from OnlySecurity courses to BSides Brighton
  • Finance, VAT and compliance across the UK and EU
  • Legal, contracts and disputes
  • Marketing and customer support
  • Hiring and building the team

How I run it

  1. Build it once, properly. Automation and shared tooling over manual effort, so a small team can run a global operation.
  2. Security is not a department. Every change gets the same scrutiny I would give a client's estate.
  3. Measure, then decide. Decisions come from the data we collect, not from assumptions.
  4. Stay hands-on. I still write code, run the infrastructure and answer the hard questions myself.

The things I've built

Ventures and brands

KSEC Worldwide →

Hands-on hardware hacking tools, embedded devices, and security-focused platforms.
KSEC EU →

The European arm of KSEC, operated from Belgium.
KSEC →

Specialist security tools, training and advisory worldwide.
OnlySecurity →

Specialist security training platform and marketplace, authored by working security professionals.
KSEC Pro Pick →

Curated range of lock picking and covert entry tools, trusted by professionals.
BSides Brighton →

Founded in 2023. A community-run security conference in Brighton, built for and by the people who attend it.

Held through The KSEC Group and Castledine Holdings, with property and capital interests under Castledine & Co.

Experience

The path here

University at 16
Began a Bachelor's degree in Computing Science after being fast-tracked from college.
2014 to 2018
IT Systems Admin and Support
Infrastructure work across SMB and SME environments.
2018 to 2021
Security Consultant
Context Information Security, now Accenture Security. Red team, web, cloud, AD and RFID engagements for global clients.
2021 to 2024
Head of Offensive Security
Informer, acquired by Bugcrowd. Senior Security Consultant, then Head of Offensive Security leading the pentest team.
2017 to now
Founder
KSEC and the subsequent ventures across the group.